

Implementing RBAC in GitLab
Role Based Access Control
2. Implementing RBAC in GitLab
Understanding Roles and Permissions
In GitLab, roles are defined with varying levels of access to projects and resources. Key roles include:
- Owner: Full control over a group and its projects. This role is available for groups, not as a project membership role.
- Maintainer: The highest standard project role, with broad control over the project and its settings.
- Developer: Access to code, pipelines, and issues but restricted from managing project settings.
- Reporter: Read-only access to the project, including issues, merge requests, and pipelines.
- Guest: Limited access, primarily for viewing project information without the ability to make changes.
Role Assignment in GitLab
Roles can be assigned at both the project and group levels in GitLab, specifying the level of access each user or group has within that scope.
Configuring Roles in GitLab
-
Navigate to Project Settings: Go to your project in GitLab and click on
Manage>Members. -
Invite members: Add users or groups and assign an appropriate role. At project level, the standard roles range from
GuesttoMaintainer; theOwnerrole applies at group level.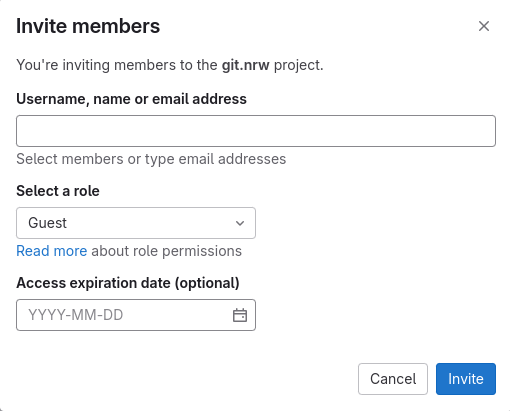
-
Review Permissions: Verify that the selected standard role grants only the permissions the member needs.
Example: Assigning Roles in GitLab
Project: My Awesome Project
Group Owner: John Doe (john.doe@example.com )
Maintainer: Jane Smith (jane.smith@example.com )
Developer: Team Developers (developers@example.com )
Reporter: Reporter (reporter@example.com )
Guest: Public Access